Who watches the watchmen?
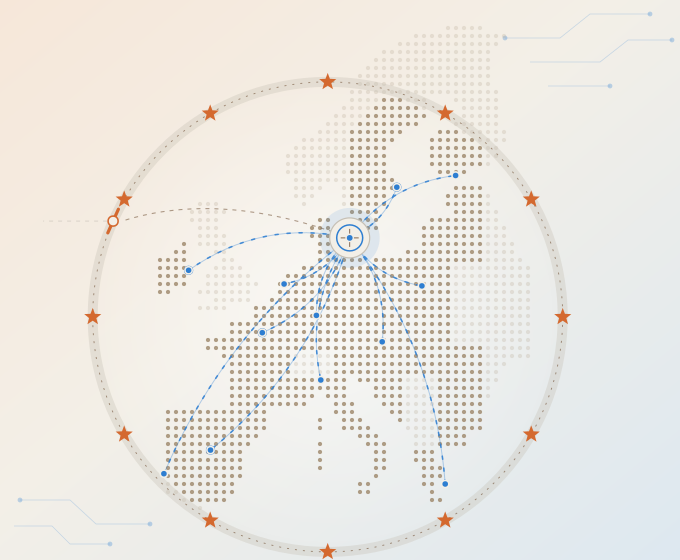
Most “sovereign AI” vendors won't tell you where their claims end. We will. Sovera is sovereign MDR built in Europe: open-weight AI on our own GPUs, in our own EU data center, with no hyperscaler in the path. It's the only kind of data sovereignty claim that survives NIS2, DORA, and GDPR scrutiny, and the only kind worth building a SOC on.
GDPR
Customer data is processed and stored under EU jurisdiction. It never transits or gets cached on a US cloud service, at any point.
NIS2
Role-based approvals, segregation of duties, and a full audit trail for every investigative action. Mapped to NIS2 access-control requirements.
DORA
An EU-domiciled ICT provider with no hyperscaler in the inference path. Less concentration risk in your third-party register.
EU jurisdiction
Copenhagen HQ, EU legal entity, Sovera-owned infrastructure. Legal domicile and governance sit fully in the EU.
Why sovereignty claims are under scrutiny
A 2026 Tech Policy Press / AI Now Institute analysis found that most European “sovereign AI” claims collapse under scrutiny: proprietary US models bundled with hyperscaler contracts, or inference capacity that subsidizes the same US labs it was meant to counter. Sovera is built differently. Analysts call it compute sovereignty: owning the critical inference infrastructure rather than renting access to it. It's a narrower, harder claim than “we use a European model.” It's also the one that matters for NIS2 and DORA-regulated buyers.
Compute sovereignty
An open-weight Mistral model served on Sovera-owned GPUs, inside a Sovera-controlled EU data center. We own the inference path. We don't rent it.
No hyperscaler in the path
No hyperscaler sits in the model-serving or customer-data path. Your data never leaves infrastructure Sovera owns and operates.
Every action auditable
An agentic framework with built-in authentication, segregation of duties, and approval controls. Every investigative action leaves an audit trail.
Typical “sovereign AI”
Sovera
The sovereignty stack, layer by layer
We could call all of this “sovereign.” We won't. Here's exactly what Sovera controls, what we don't, and what it means for your GDPR, NIS2, and DORA obligations.
Your tools are making decisions. Who's checking the decisions?
Sovereign infrastructure answers where your data lives. Governing the AI that acts on it is the other half. Our field guide, New Processes for the AI-Driven SOC, covers the five shifts behind an AI-native SOC, including why governance has to move outside the model.
Get the free ebook →Questions compliance teams ask
How does Sovera support NIS2 compliance?
How does Sovera fit DORA ICT third-party risk requirements?
Where is my data stored and processed under GDPR?
What's the difference between data residency and data sovereignty?
Is every layer of Sovera's AI sovereign?
Let's put it to the test.
No hyperscaler path, EU jurisdiction, a full audit trail, and radical transparency. Want to see how sovereign MDR fits your environment? Let's start with a conversation, not a claim.
Talk to us